RSA Authenticator (SecurID)

Screenshots
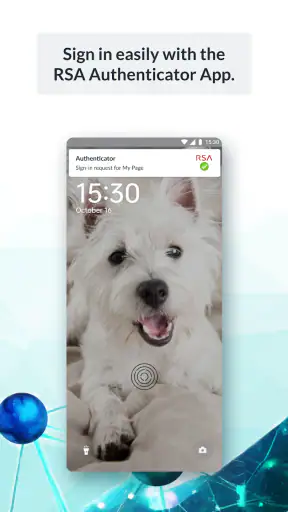
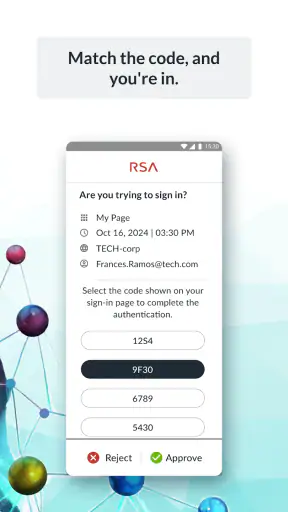
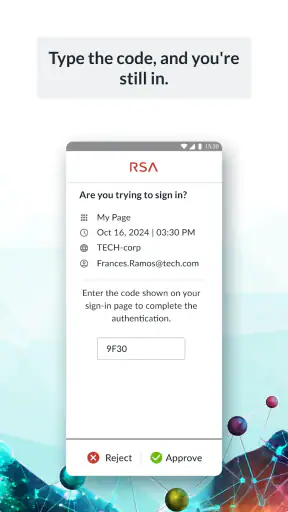
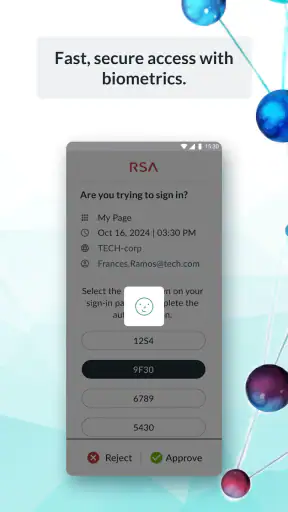
Details
- Rating
- 1.18K reviews
- Version
- 4.7.1.1
- Developer
- RSA Security
Analysis by Norviv
Signing in should not become a conversation with your phone, yet that is exactly what happens when an account asks for an extra verification step at the wrong moment. RSA Authenticator (SecurID) is built for that narrow but important part of digital communication: proving that the person entering an account is really you. I used it as a security companion rather than as a destination app, and my overall impression is practical. It can make protected sign-ins clearer and safer, but its value depends heavily on how an organization has configured it and how comfortable you are with a separate authentication step.
This is a free communication app from RSA Security, aimed at authentication rather than messaging, calling, or social interaction. Its store summary mentions passkeys, biometrics, one-time passwords, and other sign-in methods, so it sits between traditional password habits and newer passwordless workflows. The app is rated for Everyone, has passed ten million installs, and carries an average rating of 3.3 from around eighteen thousand ratings. Those figures suggest a widely used tool with a mixed everyday experience, which matches my impression: the security purpose is straightforward, while setup and account-specific behavior can determine whether the app feels smooth or frustrating.
Where RSA Authenticator fits into daily communication
The need it addresses is easy to recognize. Work accounts, remote systems, internal portals, and other protected services often require more than a username and password. Instead of treating that extra step as an interruption, I found it more useful to think of RSA Authenticator as a short checkpoint before a conversation or task can begin. It does not replace the service I am trying to reach; it helps establish trust before access is granted.
That distinction matters because the app is not equally useful to everyone. If your employer, school, or service provider specifically uses RSA authentication, installing it may be necessary. If you are simply looking for a general-purpose authenticator for unrelated personal accounts, you should first check whether those accounts support RSA Authenticator. A familiar interface cannot compensate for an authentication system that the target service does not accept.
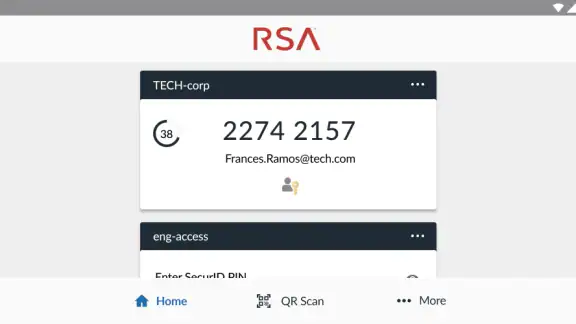
In a realistic workday, I might open a company portal before a video meeting, enter my account details, and then move to the authenticator for a passkey, biometric confirmation, or one-time password. The best version of that routine takes only a moment. The important benefit is not excitement or convenience in isolation; it is reducing uncertainty. I know which screen is asking for confirmation, what kind of response is expected, and when I can return to the original task.
That clarity becomes more valuable when communication is time-sensitive. Joining a meeting, responding to a colleague, or retrieving a document can feel unnecessarily delayed when an authentication prompt is vague. RSA Authenticator gives that verification step its own place instead of leaving the whole process hidden inside a browser or an unfamiliar login page. In my experience, separating the security action from the communication task makes the sequence easier to understand.
The app has been available since May 24, 2011, and the current version is 4.7.1.1. I mention that history because it helps explain its role: this is an established security utility, not a newly fashionable messaging product. The developer, RSA Security, is associated with identity and access tools, and the app feels designed around controlled access rather than casual discovery.
Stories Picked for You

Life360 Works Better When Your Household Agrees on What to Share

YouVersion Bible Fits Scripture into Everyday Phone Routines

Matchington Mansion Review: Match-Three Puzzles With a Place to Restore

Android Auto Shows Why Safer Driving Software Does Less

Google Find Hub Runs on Shared Devices and Quiet Trust

Sygic GPS Navigation: The Ultimate Offline Travel Companion
How the conversation flow changes
RSA Authenticator does not create a conversation, but it changes the rhythm before one begins. A normal sign-in can feel like a single action: enter credentials and continue. With an authenticator involved, the flow becomes a short exchange between the service and the phone. The service asks for proof, the app provides or confirms it, and the service allows the session to continue.
I prefer this explicit rhythm to an unclear prompt that simply says something went wrong. When the app presents a verification action, I can treat it as a deliberate pause rather than repeatedly guessing at a password. That is especially helpful when I am switching between a phone and a computer, where the login page and the authentication step live in different places.
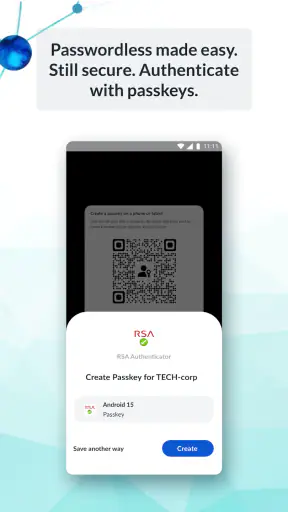
Passkeys and biometrics can make the exchange feel more natural because they reduce the need to type a temporary code. A one-time password remains useful when a service follows a more traditional two-step process. The practical trade-off is that the most convenient method may not always be the one available for a particular account. The organization behind the account controls much of that experience, so I would not judge the app solely by one login flow.
One useful habit is to complete enrollment when you are calm, connected, and not already locked out of an urgent account. Authentication setup is the wrong task to postpone until a meeting is starting. I would also keep the phone’s normal unlock method familiar, since biometric confirmation depends on the device’s own security routine. The goal is to make the verification step predictable before it becomes part of a high-pressure conversation.
Another practical insight is to identify which part of the process is failing. If the service rejects the login before the authenticator appears, the problem may be the account or the service. If the app opens but the confirmation does not complete, the issue may be the selected method, the device state, or the enrollment. Separating those stages prevents the common mistake of repeatedly entering credentials when the real problem is elsewhere.
For people who regularly move between workstations, the app can also create a healthier boundary between personal and professional attention. The phone becomes the place where identity is confirmed, while the computer remains the place where the actual work or conversation happens. That division is small, but it stops authentication from blending into every browser tab and reduces the temptation to keep sensitive account details visible on a shared screen.
The attention cost of an extra security step
Security always asks for some attention, and RSA Authenticator is no exception. Even a quick confirmation can break concentration when it arrives in the middle of writing, presenting, or responding to someone. I found the interruption easiest to accept when I knew why it was happening. The app feels less intrusive when the verification request clearly corresponds to an action I just started.
The cost becomes higher when the request is unexpected. An unexplained prompt can make a person wonder whether a session expired, whether a device is trying to connect, or whether someone else is attempting access. In that situation, the safest response is not to approve automatically. I would stop, return to the service I intended to use, and confirm that the login request matches my action. A fast approval is not a good outcome if it trains you to accept every prompt without thinking.
This is one of the app’s less obvious lessons: authentication should support attention, not consume it. I would avoid opening the app repeatedly to search for a code before checking what the login screen actually requests. If the service expects a passkey or biometric confirmation, hunting for a one-time password only adds confusion. Matching the method to the prompt keeps the interaction short and reduces mental clutter.
The separate app can also be inconvenient for people who want every task contained in one place. A built-in password manager or an operating-system passkey flow may feel more seamless for personal accounts. Those alternatives can be better when they are directly supported by the service and when you want fewer app switches. RSA Authenticator earns its place when it is part of the account’s required security design, not simply because a separate security app sounds more serious.
At the same time, the interruption can be useful as a deliberate pause. I have found that a visible confirmation step makes me more aware of what I am accessing and from which device. That awareness is valuable for work systems and sensitive information, where instant convenience is not the only measure of quality. The app changes the rhythm from “click and continue” to “verify, then continue,” and that extra beat can prevent careless access.
There is also a social dimension to this delay. If a colleague is waiting while I authenticate, I may feel pressure to rush. My advice is to treat the security step as part of the meeting’s preparation rather than an embarrassment to hide. Setting it up before the call, keeping the phone available, and recognizing the expected method can make the delay nearly invisible. The app cannot remove every interruption, but a prepared workflow keeps it from dominating the interaction.
Boundaries, devices, and account responsibility
RSA Authenticator works best when I give it a clear role: it confirms identity, while the protected service handles communication and work. That boundary helps me avoid treating the phone as a universal key that should approve anything placed in front of me. I would never approve an unfamiliar request merely because it arrives during a busy moment.
The app’s support for passkeys, biometrics, and OTP gives organizations more than one way to structure that boundary. A biometric confirmation can be quick and private on a personal phone. A one-time password can be more familiar to someone who prefers to read and enter a code. Passkeys can reduce dependence on memorized passwords. Each method has a different attention pattern, so the best choice is the one that fits the account’s risk, device habits, and support process.
For a shared or managed device, I would be more cautious. Authentication apps are closely tied to personal access, and handing the phone to another person can blur responsibility. The app is not a substitute for account ownership rules or an organization’s recovery procedure. Before changing phones or resetting a device, I would make sure I understand how the associated account will be restored. Losing access to the authentication step at the same time as needing the account is an avoidable problem.
This is where the app may not suit someone who wants a completely self-directed setup. RSA Authenticator can be part of a larger identity system, and the organization controlling that system may determine enrollment, recovery, and available methods. If you expect to install an authenticator and independently connect it to any account you choose, you may find the experience more limited than a general authenticator designed around personal control.
Privacy and attention boundaries also involve notifications. A verification request should be treated as sensitive, especially if its wording or timing is unfamiliar. I would avoid discussing codes aloud in a public place and would not copy them into a chat just to save time. The app’s usefulness depends partly on disciplined habits around it. A secure tool can still be weakened by forwarding a code, approving blindly, or leaving an unlocked phone unattended.
Another trade-off concerns accessibility and speed. Biometrics may be convenient for one person and awkward for another, while typing an OTP may be easier in a particular environment. A method that works perfectly at a desk may feel clumsy when traveling or wearing gloves. I would test the expected route in the situations where I actually sign in, rather than assuming the quickest demonstration will be the quickest daily workflow.
Who should use it, and who should look elsewhere
I would recommend RSA Authenticator to people whose organization or service explicitly relies on RSA Security authentication. It is a sensible fit for employees who need a separate confirmation step before opening work systems, especially when passkeys, biometrics, or one-time passwords are available through their account. It also suits users who appreciate a clear divide between the device used for communication and the device or browser used for work.
I would be less enthusiastic about it for someone seeking a universal personal authenticator without any RSA-specific requirement. In that case, a password manager with built-in passkeys or a general OTP application may offer a more direct setup and a broader account workflow. The right alternative depends on the services you use, but the key question is simple: does the account specifically expect RSA Authenticator, or are you choosing it without a compatibility reason?
People who dislike app switching should also consider the daily rhythm. The extra step is worthwhile when it protects an important account and remains predictable. It is less appealing when the account already offers a secure, integrated passkey experience that works naturally on the same device. I would choose the method that gives strong protection without encouraging rushed approvals or repeated failed attempts.
The age rating of Everyone makes the app broadly approachable, but that does not mean every setup is equally simple. The security concepts are understandable, while enrollment and recovery can still require patience. A first-time user should expect to follow the organization’s instructions carefully and should keep a backup plan for contacting the relevant administrator or support channel if access becomes stuck.
My verdict on a quieter, clearer login routine
After using RSA Authenticator as an access companion, I see its strongest quality as structure. It gives authentication a defined moment before communication begins, which can improve clarity and prevent passwords from carrying the entire burden of account security. Passkeys, biometrics, and OTP support cover different habits, and the free price removes a direct financial barrier for people who need this particular tool.
Its weaknesses are just as practical. The experience can depend on an organization’s configuration, the extra step can interrupt concentration, and users who want a universal personal authenticator may prefer another category of app. A 3.3 average from around eighteen thousand ratings reflects that this is not a universally effortless experience, even though more than ten million installations show that it is widely relied upon.
My recommendation is therefore conditional but positive: use it when RSA Security is part of the account system you need to access, prepare the enrollment before an urgent meeting or deadline, and learn which verification method your service expects. Do not approve unexpected requests simply to keep a conversation moving. The best authentication routine is the one that protects access while keeping your attention available for the people and work waiting on the other side.
RSA Authenticator (SecurID) is not an app I would open for entertainment or casual communication, and that is not its job. Its success is measured in calmer sign-ins, fewer ambiguous prompts, and a clearer boundary between proving who I am and actually getting on with the conversation. For the right account, it is a useful and established tool from RSA Security; for the wrong account, it is unnecessary friction. Knowing that difference is the most important part of deciding whether to install it.
Frequently Asked Questions
01What is RSA Authenticator (SecurID) used for?
RSA Authenticator, also known as SecurID, is a security app used for multi-factor authentication. It helps verify your identity when signing in to supported company systems, VPNs, cloud services, and business applications. Instead of relying only on a password, the app generates or receives a secure authentication method that adds an extra layer of protection to your account.
02How does RSA Authenticator generate authentication codes?
After it has been registered with an organization’s RSA SecurID service, the app can provide authentication information such as time-based one-time passwords or approve certain login requests, depending on the company’s configuration. Codes are temporary and normally expire quickly, so they should not be shared with anyone. The exact sign-in process may vary between organizations.
03Can I use RSA Authenticator without an employer or organization account?
Usually, no. RSA Authenticator is primarily intended for users whose employer, school, bank, or other organization uses RSA SecurID authentication services. Installing the app alone does not create an account or enable authentication. You generally need an activation link, QR code, registration code, or setup instructions supplied by the organization’s IT or security administrator.
04What should I do if I change or lose my phone?
If you replace your phone, lose it, or reset it, your RSA Authenticator registration may not transfer automatically. Contact your organization’s help desk or RSA administrator as soon as possible so they can disable the old device and provide a new activation method. Avoid deleting the app or resetting your phone before confirming that you can register the authenticator again.
05Is RSA Authenticator safe, and what permissions does it require?
RSA Authenticator is designed to protect sign-ins using encrypted authentication data and temporary security codes. Depending on the version and your organization’s setup, it may request access to the camera for scanning a QR code, notifications for approval prompts, or device security features. Download it only from the official app store and never disclose activation codes, passcodes, or one-time passwords.


